Loading
New app: Spunto
Abstract
Please introduce the functions and usage of your app in summary, and also attach some screenshots.
Spunto is a native Android notes app for quick capture, Markdown, checklists, nested #labels, local search and revision history. Capture, editing and search work offline without an account. Optional synchronization connects it to the independently runnable, self-hosted Spunto server, which also provides a web client, authenticated note/space sharing and an MCP endpoint for agents. The public server release is 2026.10.1; no private cloud component is required.
The core is licensed AGPL-3.0-only. AI and SSO are optional server features: users can run their own services or omit them entirely. The Android client does not bundle a provider-specific AI/SSO vendor SDK or an advertising/analytics SDK. QR pairing uses Android camera APIs and ZXing; optional dictation uses the installed Android speech-recognition service, whose availability and privacy policy apply. Neither AI nor a proprietary hosted service is required for local note use.
- Public source and app overview
- License, privacy policy and issue tracker
- Upstream Fastlane metadata:
en-USandit-IT, descriptions, icon, screenshots and code-specific changelogs. The app interface is currently English.
Four screenshots (fictional example notes)
- Capture and timeline
- Offline label search
- Note, checklist and history controls
- Nested labels and views
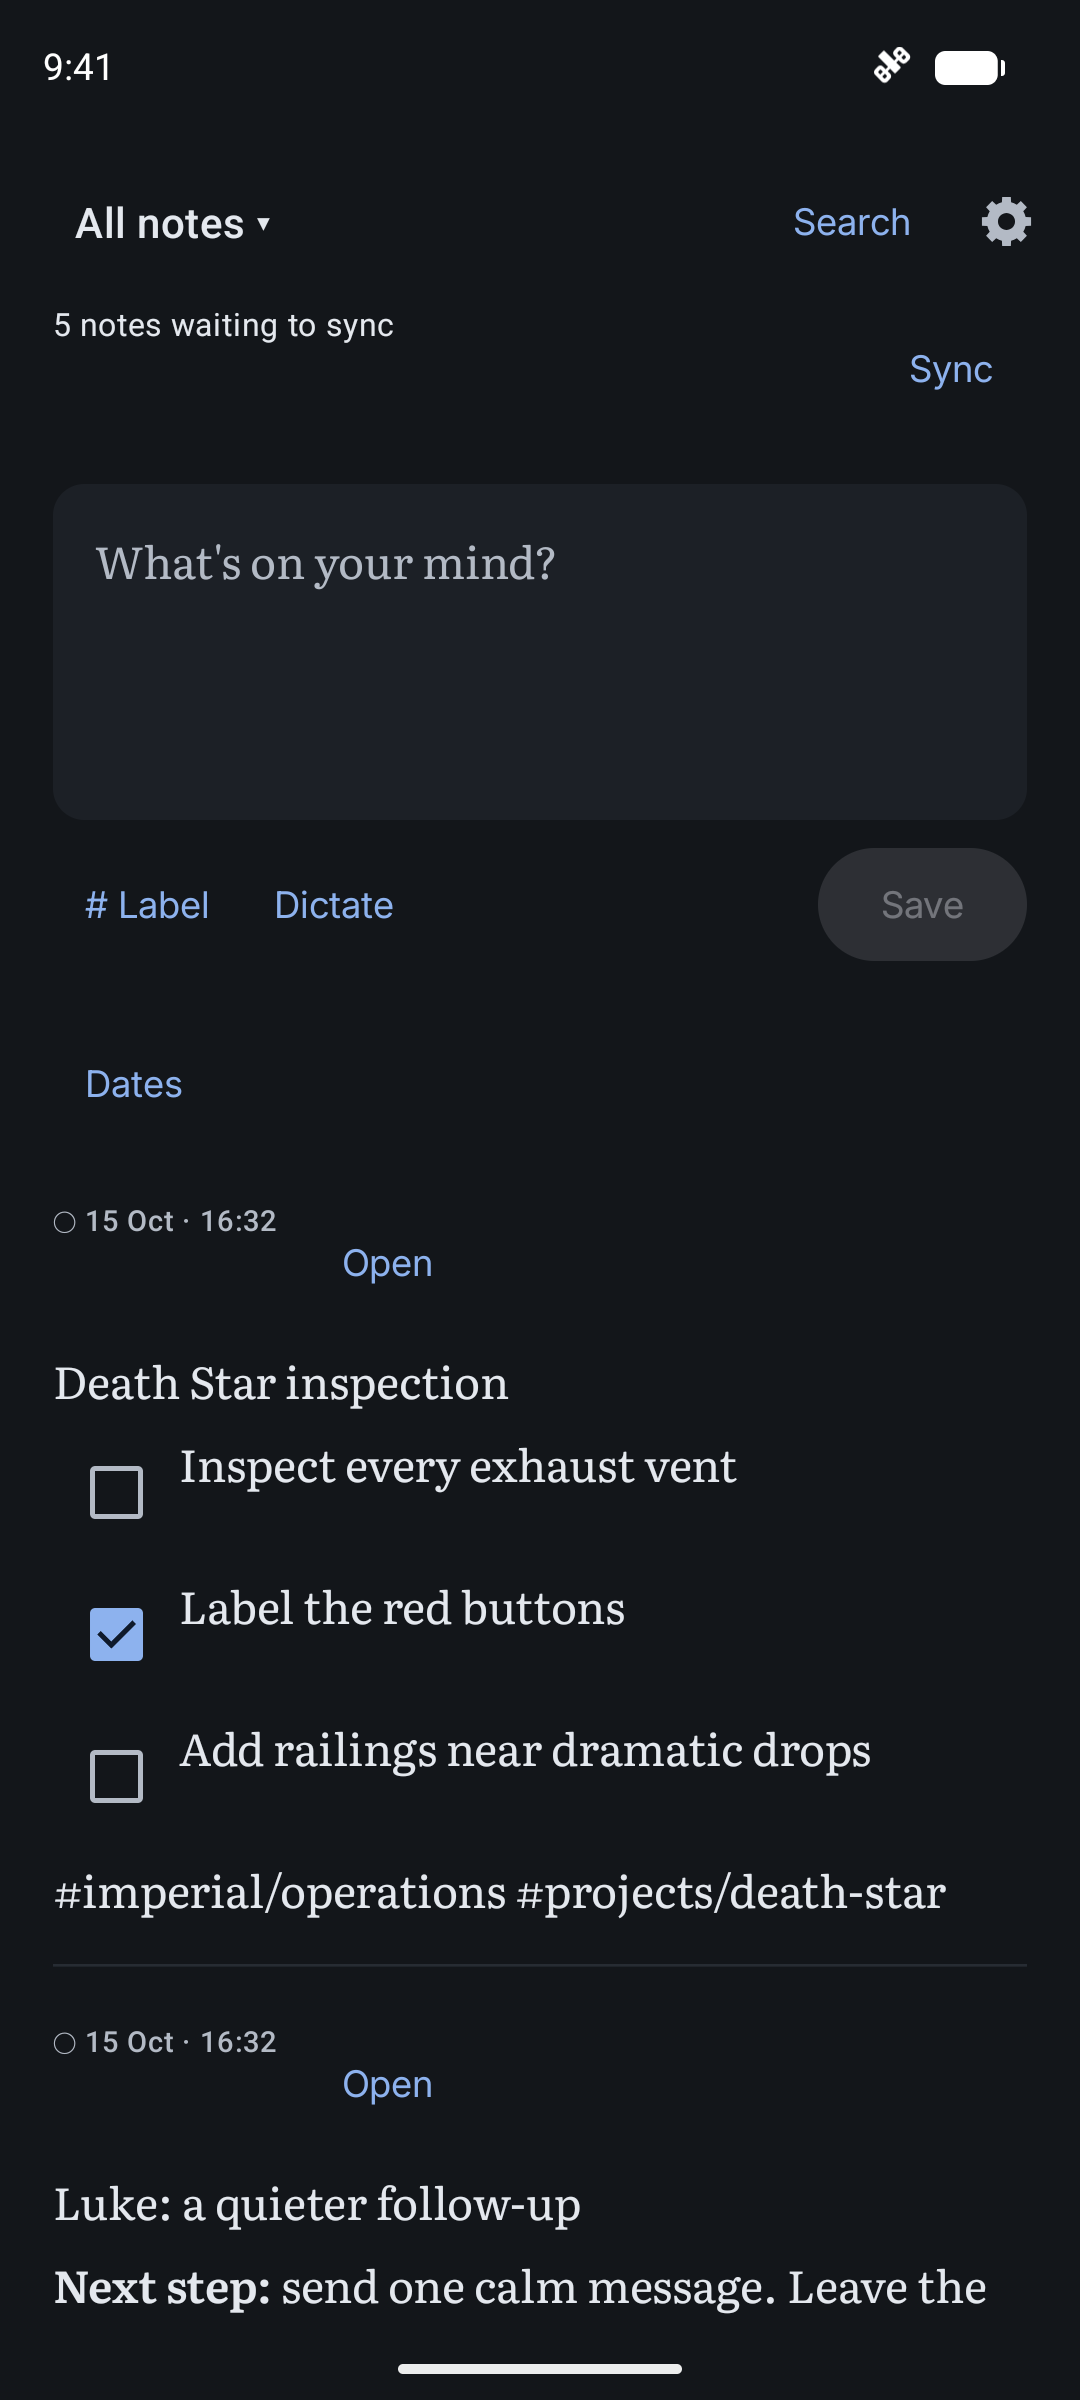
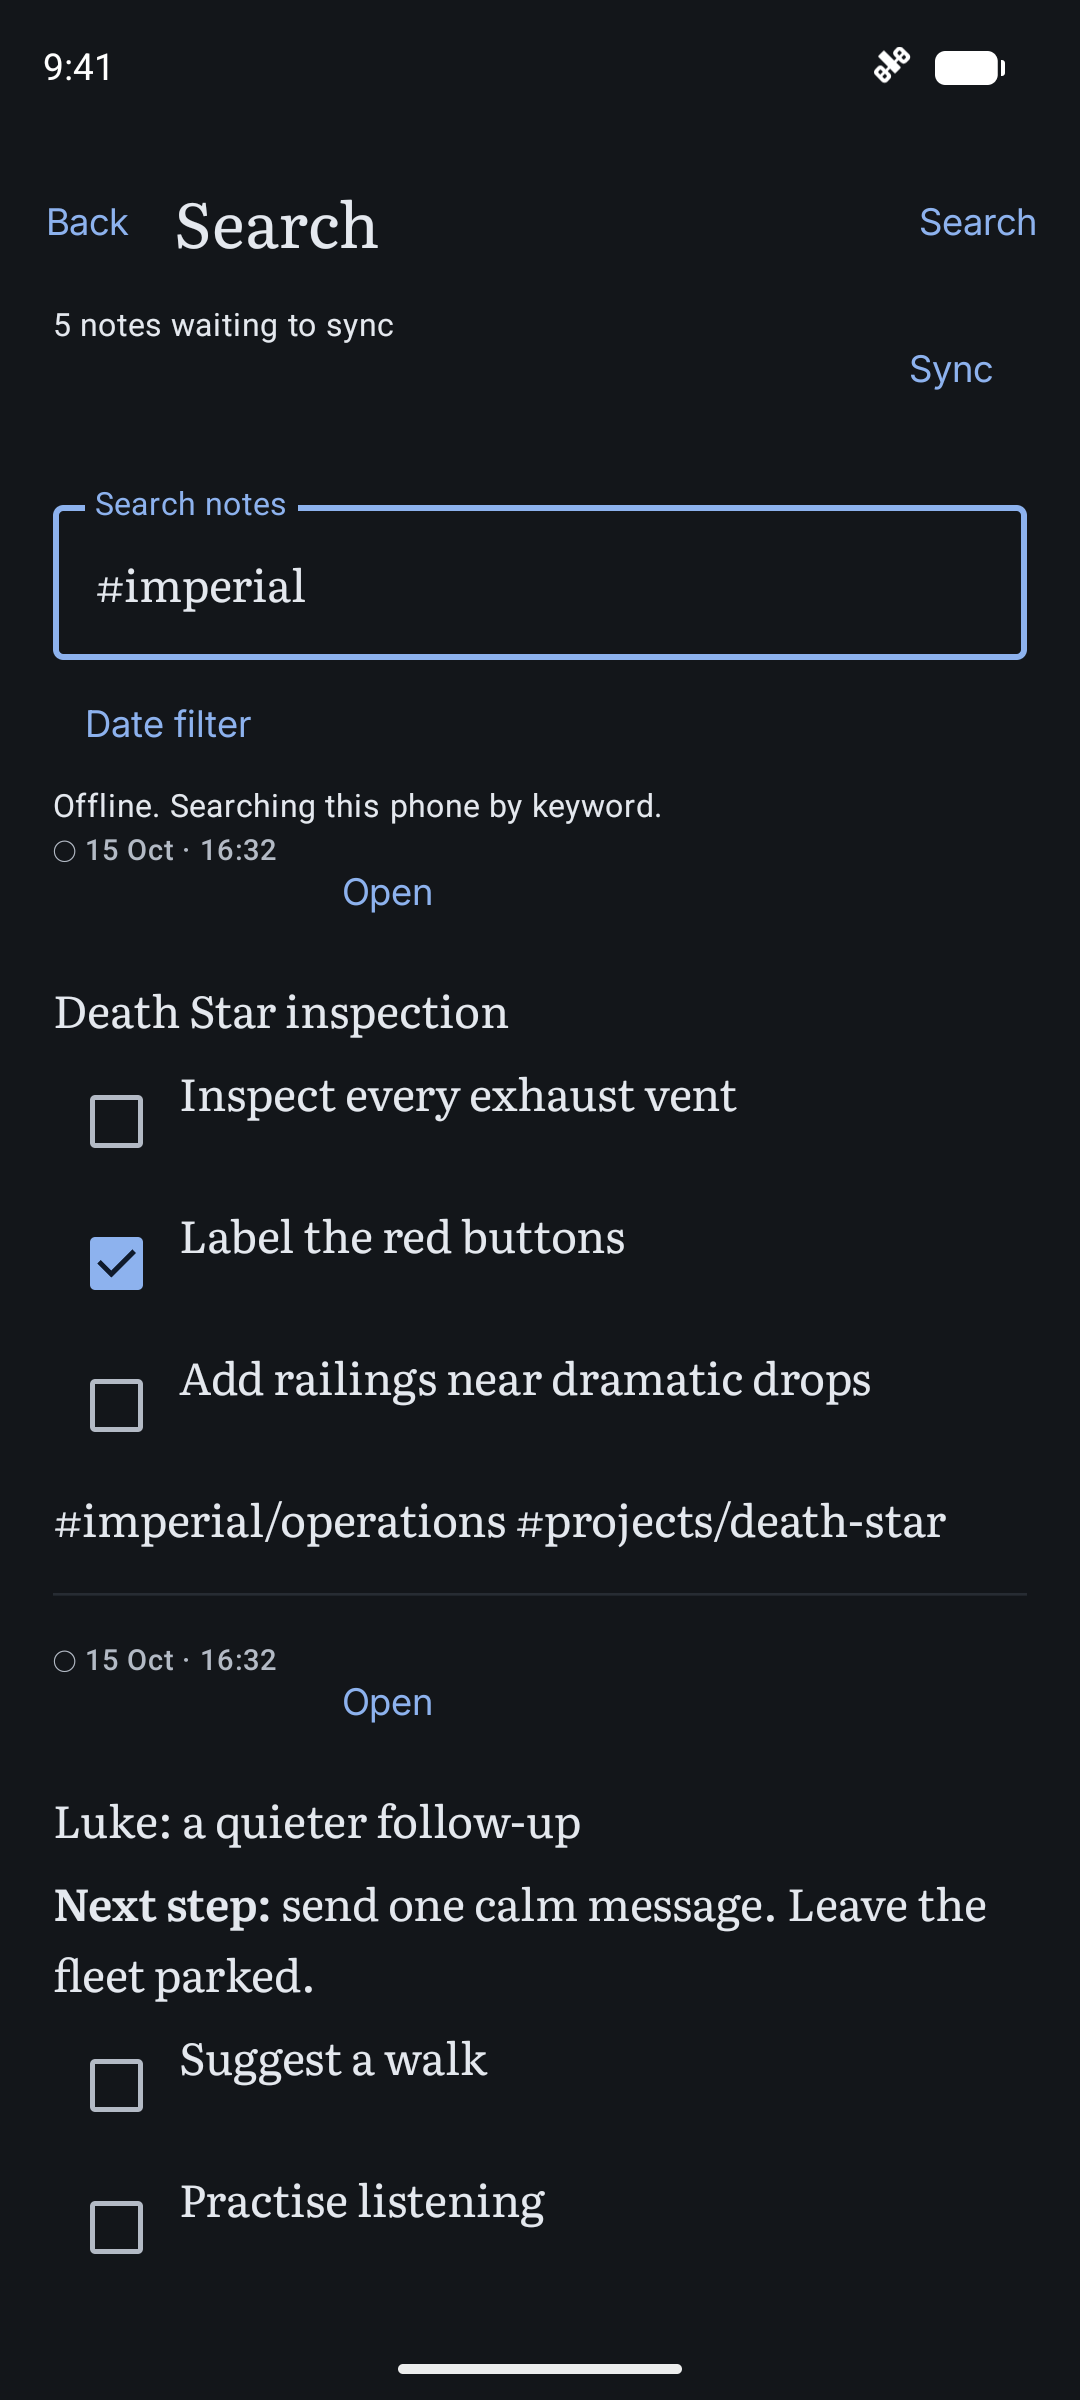
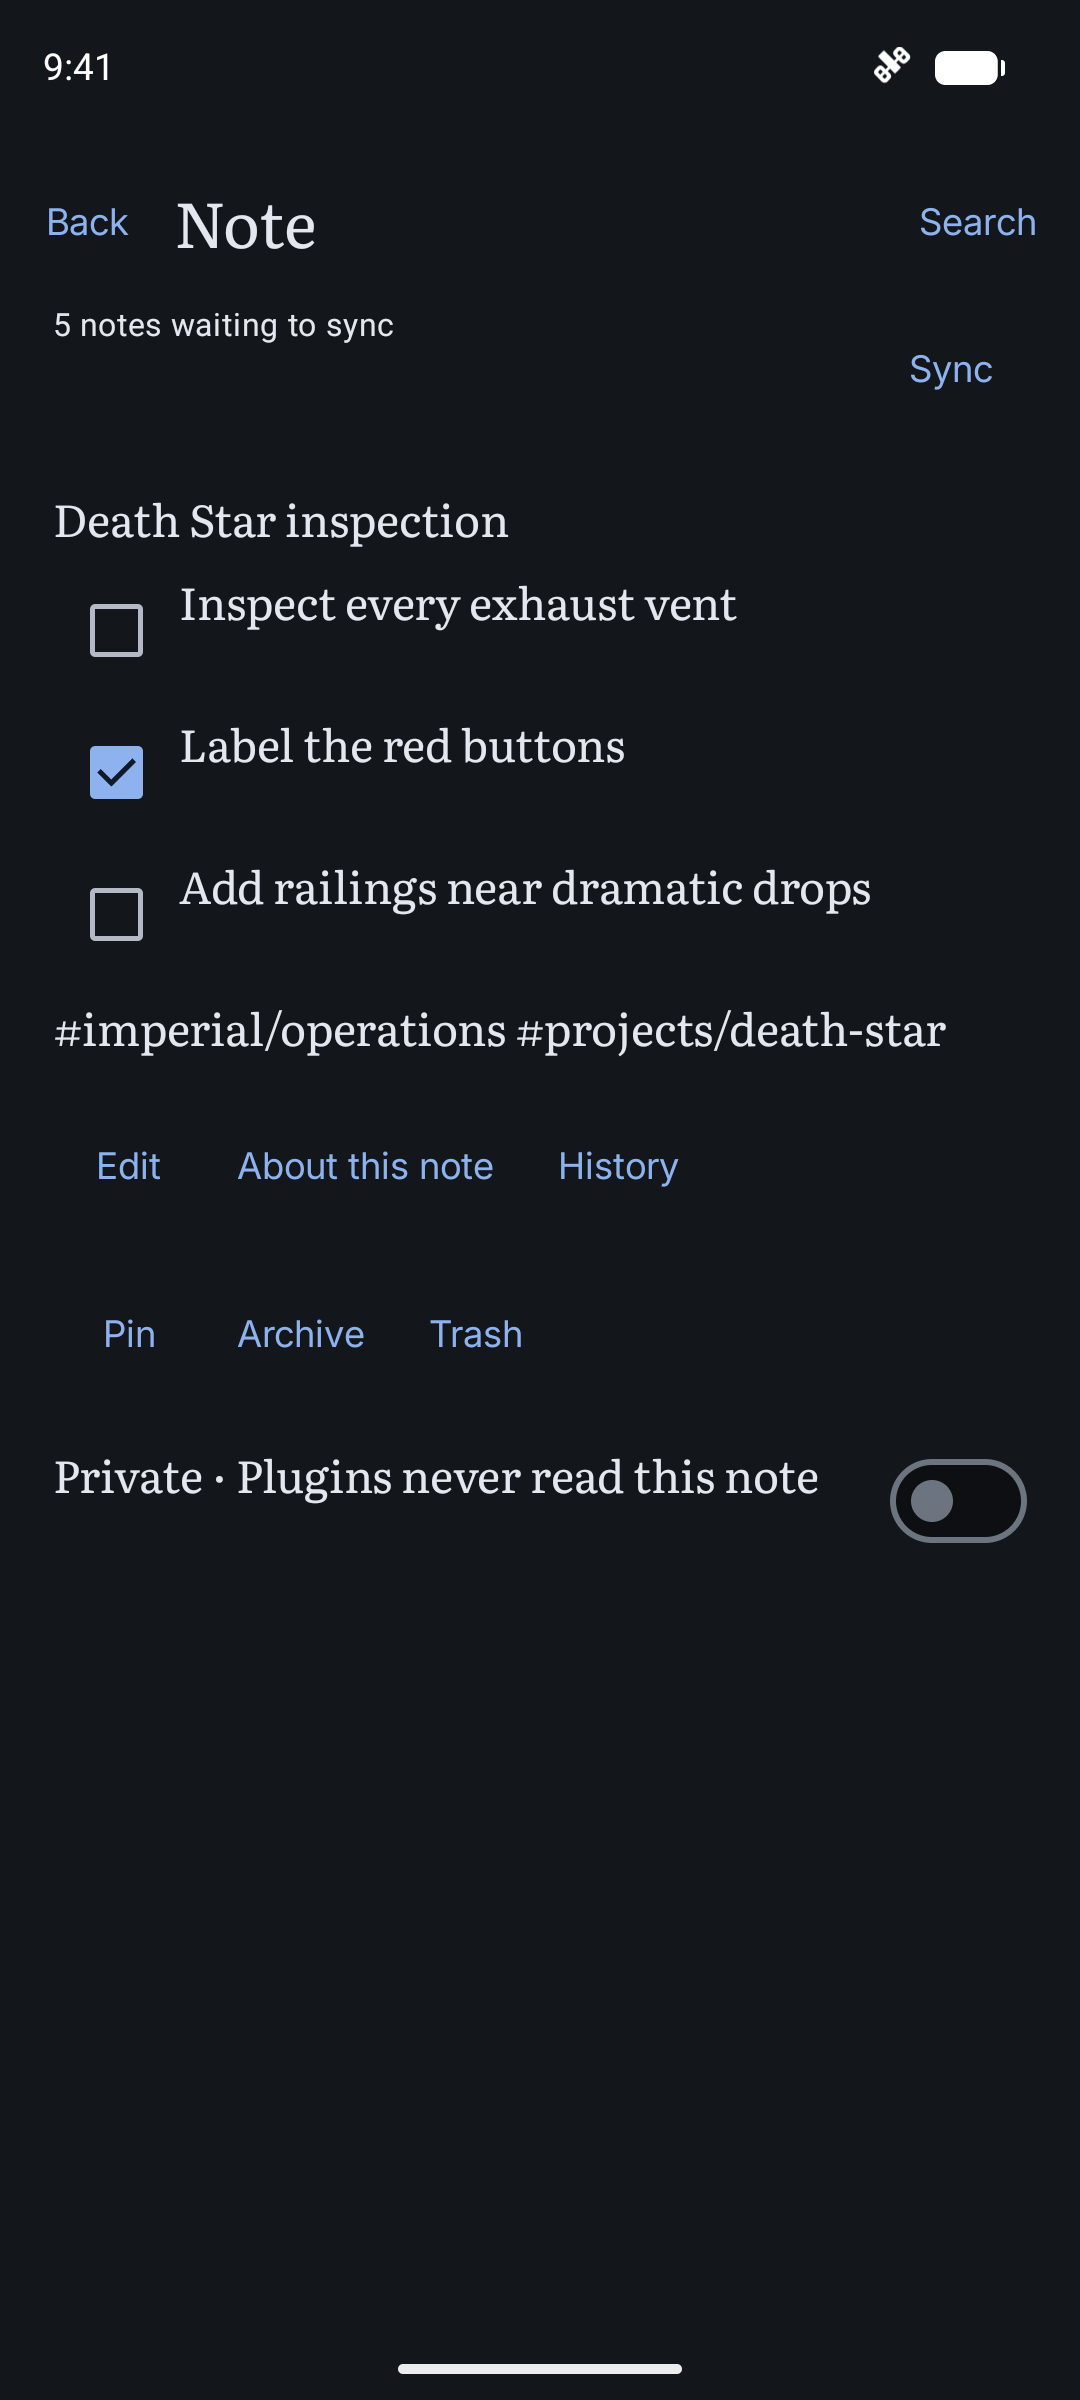
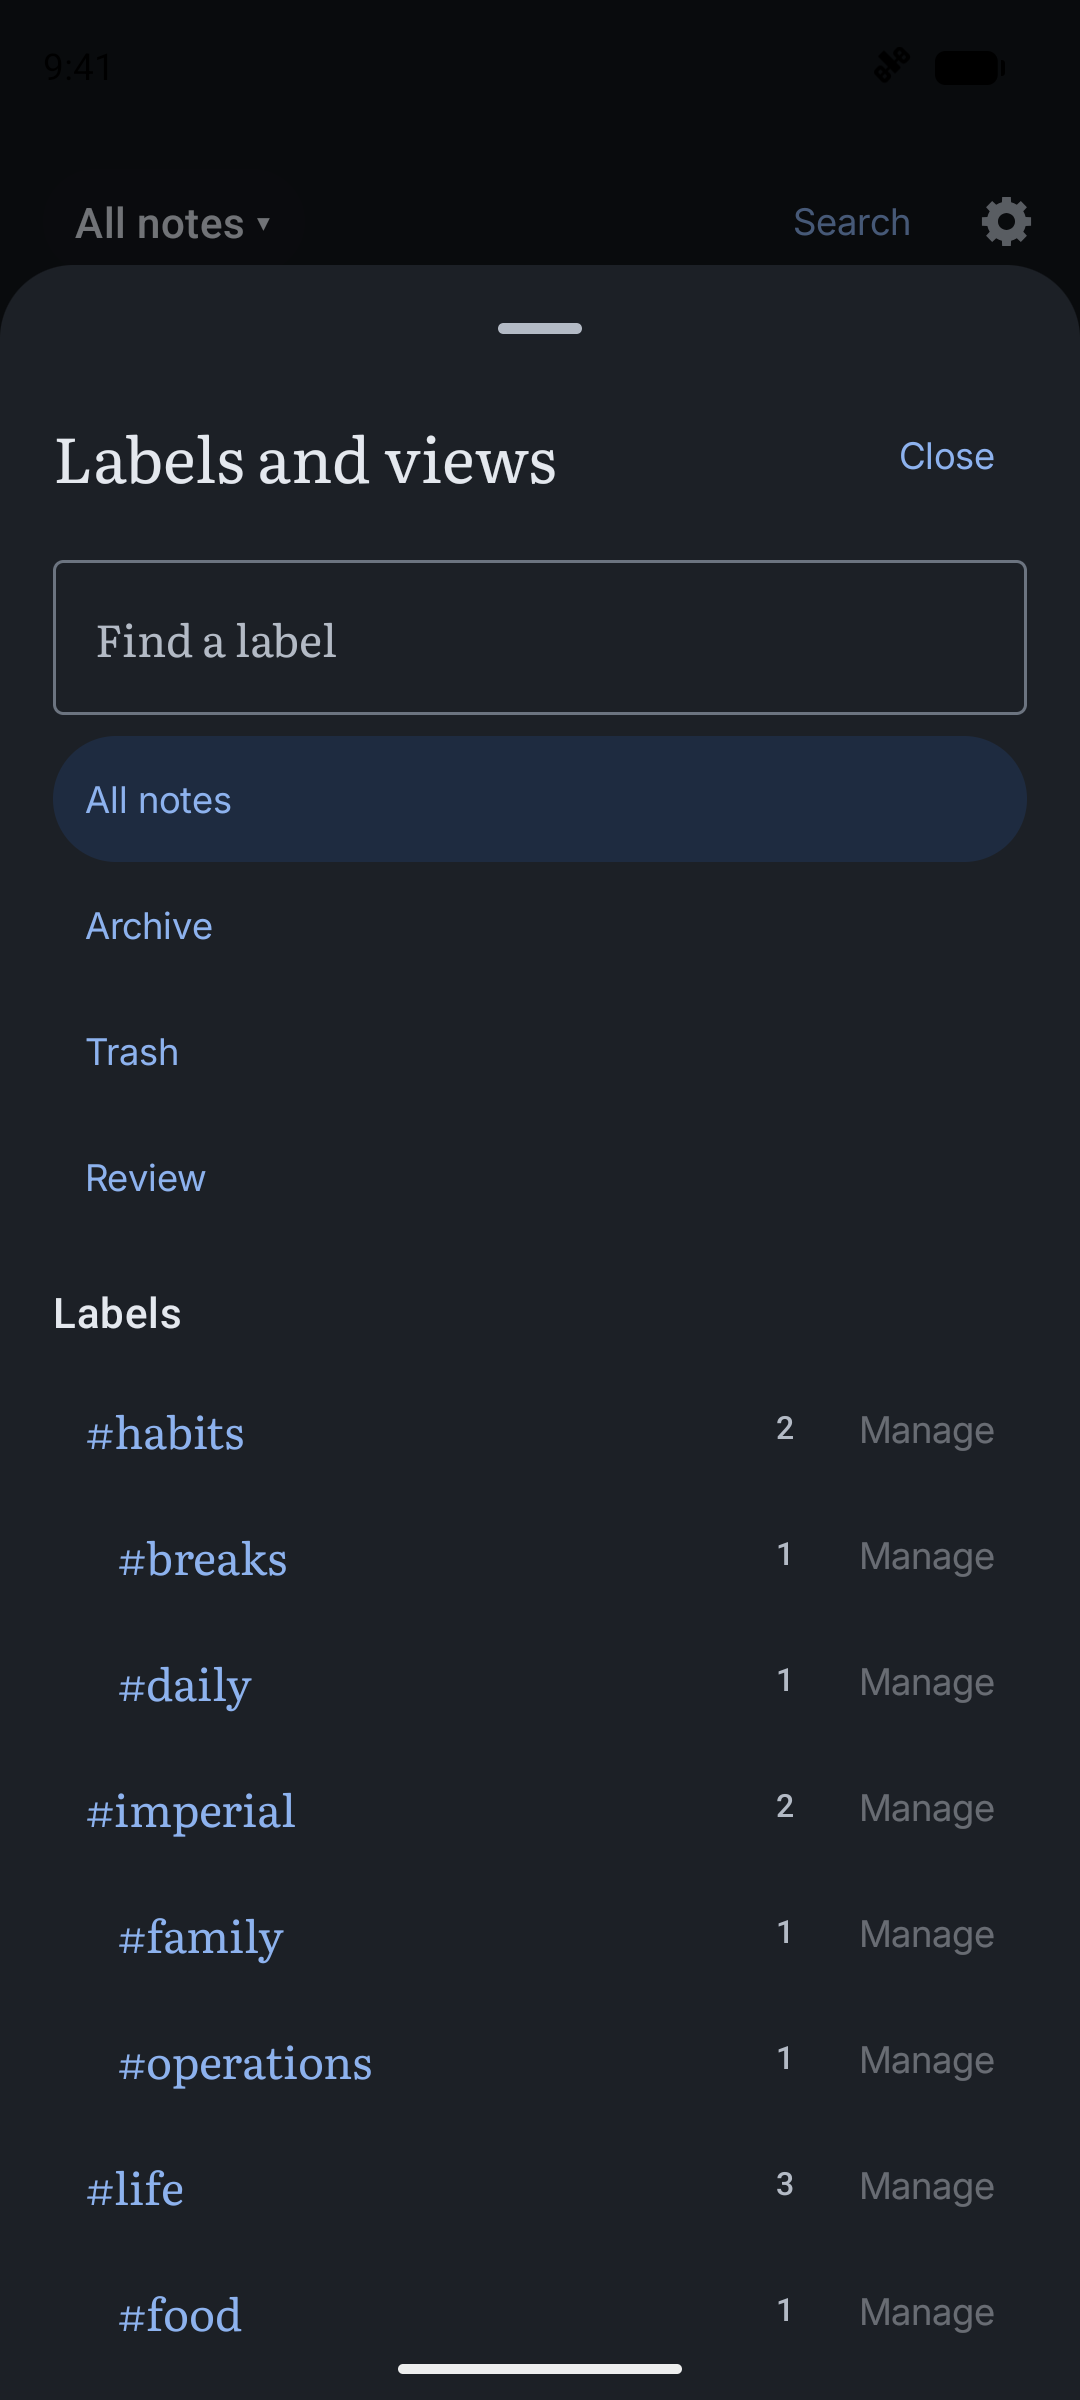
The screenshots contain fictional sample notes, not personal notes or account credentials. The same English-interface images accompany both metadata locales.
Please elaborate why you wrote this app. Please highlight the unique functions it provides over other similar apps in F-Droid.
Spunto was written to make loose ideas easy to capture and find again while keeping the library under the user's control. Labels live in the note text, including nested paths, rather than requiring folders or a project setup step. Its focus is the combination of an independent offline Android client, optional self-hosted web/sync/collaboration, and optional plugins for context packs, a decision journal and AI assistance. The core remains usable with every plugin and AI provider off.
I maintain the upstream project as vitofico and authorize its inclusion in F-Droid. This contribution is submitted from the vituzz GitLab account.
Release identity and verification status
The requested first public Android version is 2026.10.19.3, version code 14, package io.theficos.spunto (Android 8 / API 26 or newer). Versions use daily CalVer YYYY.MM.DD.RUN; Android version codes increase independently. Update checks select android/<CalVer> tags, excluding monthly server releases and debug variants.
| Item | Value / evidence |
|---|---|
| Public source repository | https://github.com/vitofico/spunto |
| Android release source, full 40-character SHA | cc03353280d9180ac63ad83da526f4f264e5c5fe — also pinned in the fdroiddata build recipe. |
| Android release tag | android/2026.10.19.3 — verified against the final source SHA above. |
| Developer-signed reference APK | spunto-2026.10.19.3.apk — anonymously downloaded and verified against the signed APK hash below. |
| Developer certificate SHA-256 | 27799072ba669055e4451cb07af03548658505a9399743a51b62c221bb45cc86 |
| Signed APK SHA-256 | b4130f35f3883866c6e194f5b7b8cabbcf1c1df8a8d28dbf504ea682b46be3c4 |
| F-Droid metadata file | metadata/io.theficos.spunto.yml |
| Metadata and update checks | readmeta, rewritemeta, lint, checkupdates and YAML 1.2/schema validation passed. Update detection resolved version 2026.10.19.3 / code 14 to the pinned source. |
| F-Droid scanner | Source scanning and the reference APK scan passed. |
| Build and reproducibility | Both the local official-toolchain build and the GitLab-hosted F-Droid build succeeded, matched the public reference binary and verified its allowed signing certificate. |
| GitLab pipeline | 2963440385: passed — all 12 jobs. Metadata-only commit: af4ef031f59b5ea808ce53c59bca2ae41672c2e3. |
| Related RFP / fdroiddata issues | No matching issues found in either tracker on 19 October 2026; search scope and links below. |
The recipe enables reproducible verification with Binaries and AllowedAPKSigningKeys, preserving the developer signing identity across GitHub, Obtainium and a future accepted F-Droid build. Two independent clean local Android builds also reproduced the developer-signed APK byte for byte. No F-Droid listing or acceptance is claimed.
Upstream checks
- Release validation and publication: passed.
- CodeQL: passed; no open code-scanning alerts at the final source.
- Security: passed.
The fdroiddata GitLab pipeline also passed, including its hosted rebuild, reference-binary reproduction and APK inspection.
Reports: manifest permissions and cleartext support
The successful check apk job reports three minor permission items and one major cleartext-traffic item. These are intentional features of Android 2026.10.19.3 / code 14:
INTERNETsupports optional synchronization and requested features on the user's chosen Spunto server. Capture, editing and local search work without a server or account.ACCESS_NETWORK_STATEsupports network-aware background sync.CAMERAis requested when the user chooses to scan a pairing QR. Frames are decoded locally; the scanner does not save or upload them. Users can paste the pairing code instead, without camera access.RECORD_AUDIOis requested for optional dictation or Voice memos. Dictation prefers the installed on-device recognizer; online recognition fallback requires separate consent and follows the speech service's policy. Dictation saves text; a Voice memo deliberately retains an audio attachment that may sync to the selected server. This permission is not used for unattended background recording.android:usesCleartextTraffic="true"intentionally permits HTTP for operator-controlled self-hosted servers, for example on a private LAN. HTTPS is supported and recommended for remote access. An HTTP connection displays Not encrypted, explicitly warns that the password and notes cross the network unencrypted, and requires Connect on this network. The API client and saved authentication configuration require the associatedhttpConsent; changing the URL or importing a pairing QR resets the UI consent. This is application consent, not a platform HTTP prohibition: the manifest permits cleartext application-wide, and there is no technical restriction to LAN addresses. Users can deliberately approve an HTTP endpoint, accepting its unencrypted transport risk.
The informational WAKE_LOCK, RECEIVE_BOOT_COMPLETED and FOREGROUND_SERVICE entries come from AndroidX WorkManager used for queued/background sync. USE_BIOMETRIC and legacy USE_FINGERPRINT support optional app lock through AndroidX Biometric. AndroidX Core supplies the app-specific non-exported dynamic-receiver permission. These are not advertising or analytics permissions.
The report's certificate, size/ABI and R8-marker entries are informational; the reference APK's allowed developer signing identity and reproducible build were verified separately. The Fastlane report has only two informational locale entries (en-US, it-IT), with no metadata issues.
CI environment warnings are separate from app findings: the config.yml mode warning concerns F-Droid's repository/tool configuration, not Spunto's installed credentials or this metadata-only contribution. Androguard's API-35-to-28 warning concerns its permission/resource lookup table; it does not change the APK's actual API-35 target. Python clint invalid-escape SyntaxWarnings and the optional qr manual-page warning originate in the CI tool packages. No Spunto source or APK change is required for those tool-environment messages.
Source references: HTTP warning and consent, API transport guard, authentication persistence guard, and privacy policy.
Related issues
Read-only GitLab API searches covered publicly visible issue titles/descriptions in all issue states in both fdroiddata and RFP on 19 October 2026. Each tracker was searched for spunto, io.theficos.spunto and vitofico/spunto; all six searches returned zero issues with no additional result pages. There are no matching issue numbers to reference from this search.
Checklist
Policy
- The app complies with the inclusion criteria.
- The original app author has been notified (and does not oppose the inclusion). If you are not the author, please paste the link of the reply from the author.
- The upstream app source code repo contains the app metadata in a Fastlane or Triple-T folder structure. The summary and description must be included and images, icon, and changelog should also be provided for better user experience. The
en-USlocale must be included.
Docs
- Please read the guide first if this is your first contribution.
- Please make sure your metadata follows the best practice in our templates.
- Please read the Build Metadata Reference and make sure your metadata is valid.
- Please read the Quick Start Guide.
Merge Request Setup
- The title of this merge request should follow "New app: app name" format.
- Please make sure your fdroiddata fork is public and your branch is not protected. See https://docs.gitlab.com/user/project/repository/branches/protected/.
- Please read our Git guide if you don't know how to rebase your branch. Don't rebase your branch if there is no conflict.
- All related fdroiddata and RFP issues have been referenced in this merge request
- Please only submit one app in one MR.
Metadata
- Metadata must be put in
metadata/<applicationId>.yml. - Metadata must be a valid YAML file.
- Metadata must use LF as line ending.
- Don't add summary/description/changelog/images or anything that should be provided in upstream repo. Please check the Changes tab to make sure there is no other unrelated files added in the MR.
- Releases are tagged and auto update is enabled unless there is a special reason.
- There is an issue tracker and contact info of the author so that we can report bugs and contact the author.
- An AuthorName must be added. It doesn't need to be the real name.
- External repos are added as git submodules instead of srclibs. You can update git submodules without opening an MR in this repo and the submodule is covered by our scanner.
- Enable Reproducible Builds. We'll use your signature for improved security/reliability, also allowing users to switch between different channels. Do note that if you don't enable reproducible build then the apk will be signed with our key so you can't enable it later. If you can't enable this, please add the reasons here.
- Setup abi split if the APK is large and the splitted ones can be much smaller.
- Only the latest versions should be kept in the metadata before it's merged. If you update the metadata, please replace the old versions with the new ones.
- Don't add any disabled versions in the metadata.
- The
commitfield should be the full hash. Please don't use tag or branch in commit.
Not applicable: there are no external source repositories or srclibs. The universal APK is 4,492,353 bytes (4.49 MB); ABI splits are unnecessary.
Pipeline
- All pipelines should pass.
- All warnings and errors in the Reports tab should be fixed or explained.
- F-Droid CI runners are under GitLab's FOSS program, so there's no need for you to pay for any CI time. If Gitlab starts asking for phone numbers or credit cards don't submit anything, just leave a note in the MR so we know we need to trigger the CI.